Connect Okta to SurrealDB to allow members of your organisation to sign in with their Okta credentials. You create an OpenID Connect app integration in the Okta Admin Console, then enter its details in a new connection in SurrealDB Studio.
Before you start, verify the email domain your company uses. You also need an Okta account that can create app integrations.
Step 1: Create an app integration
In the Okta Admin Console, open Applications and Resources, then Applications.
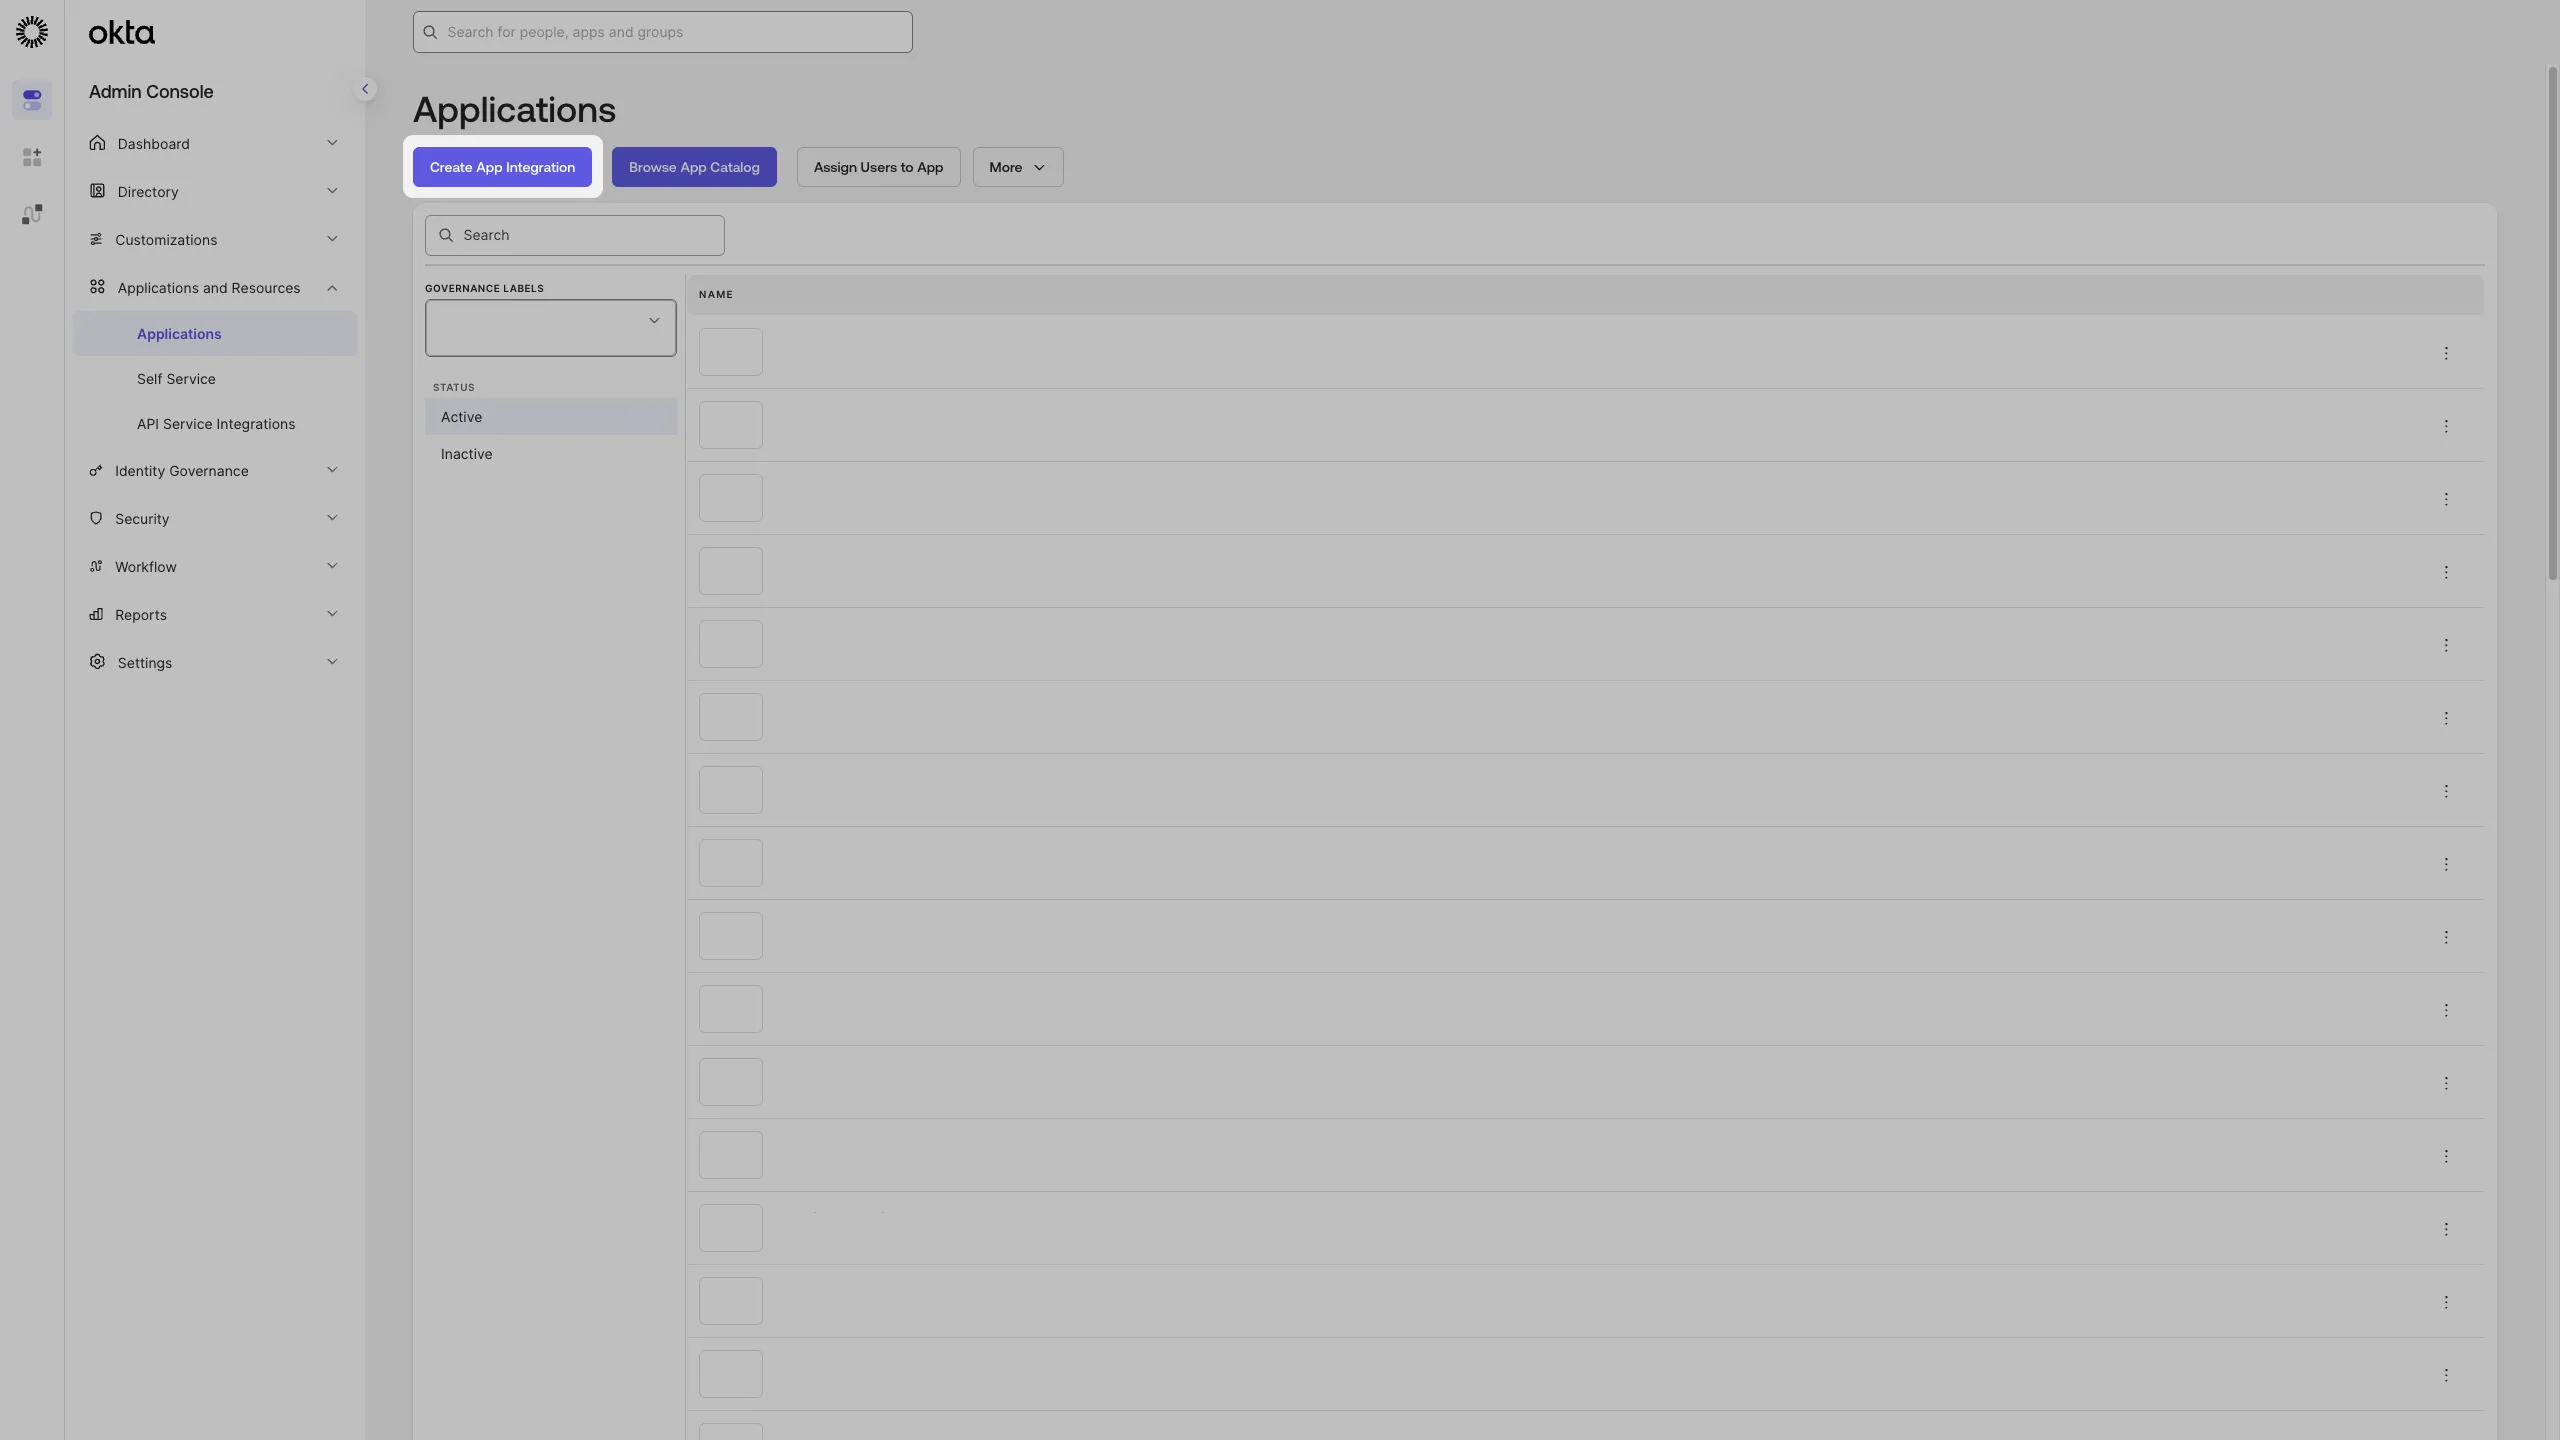
Select Create App Integration.
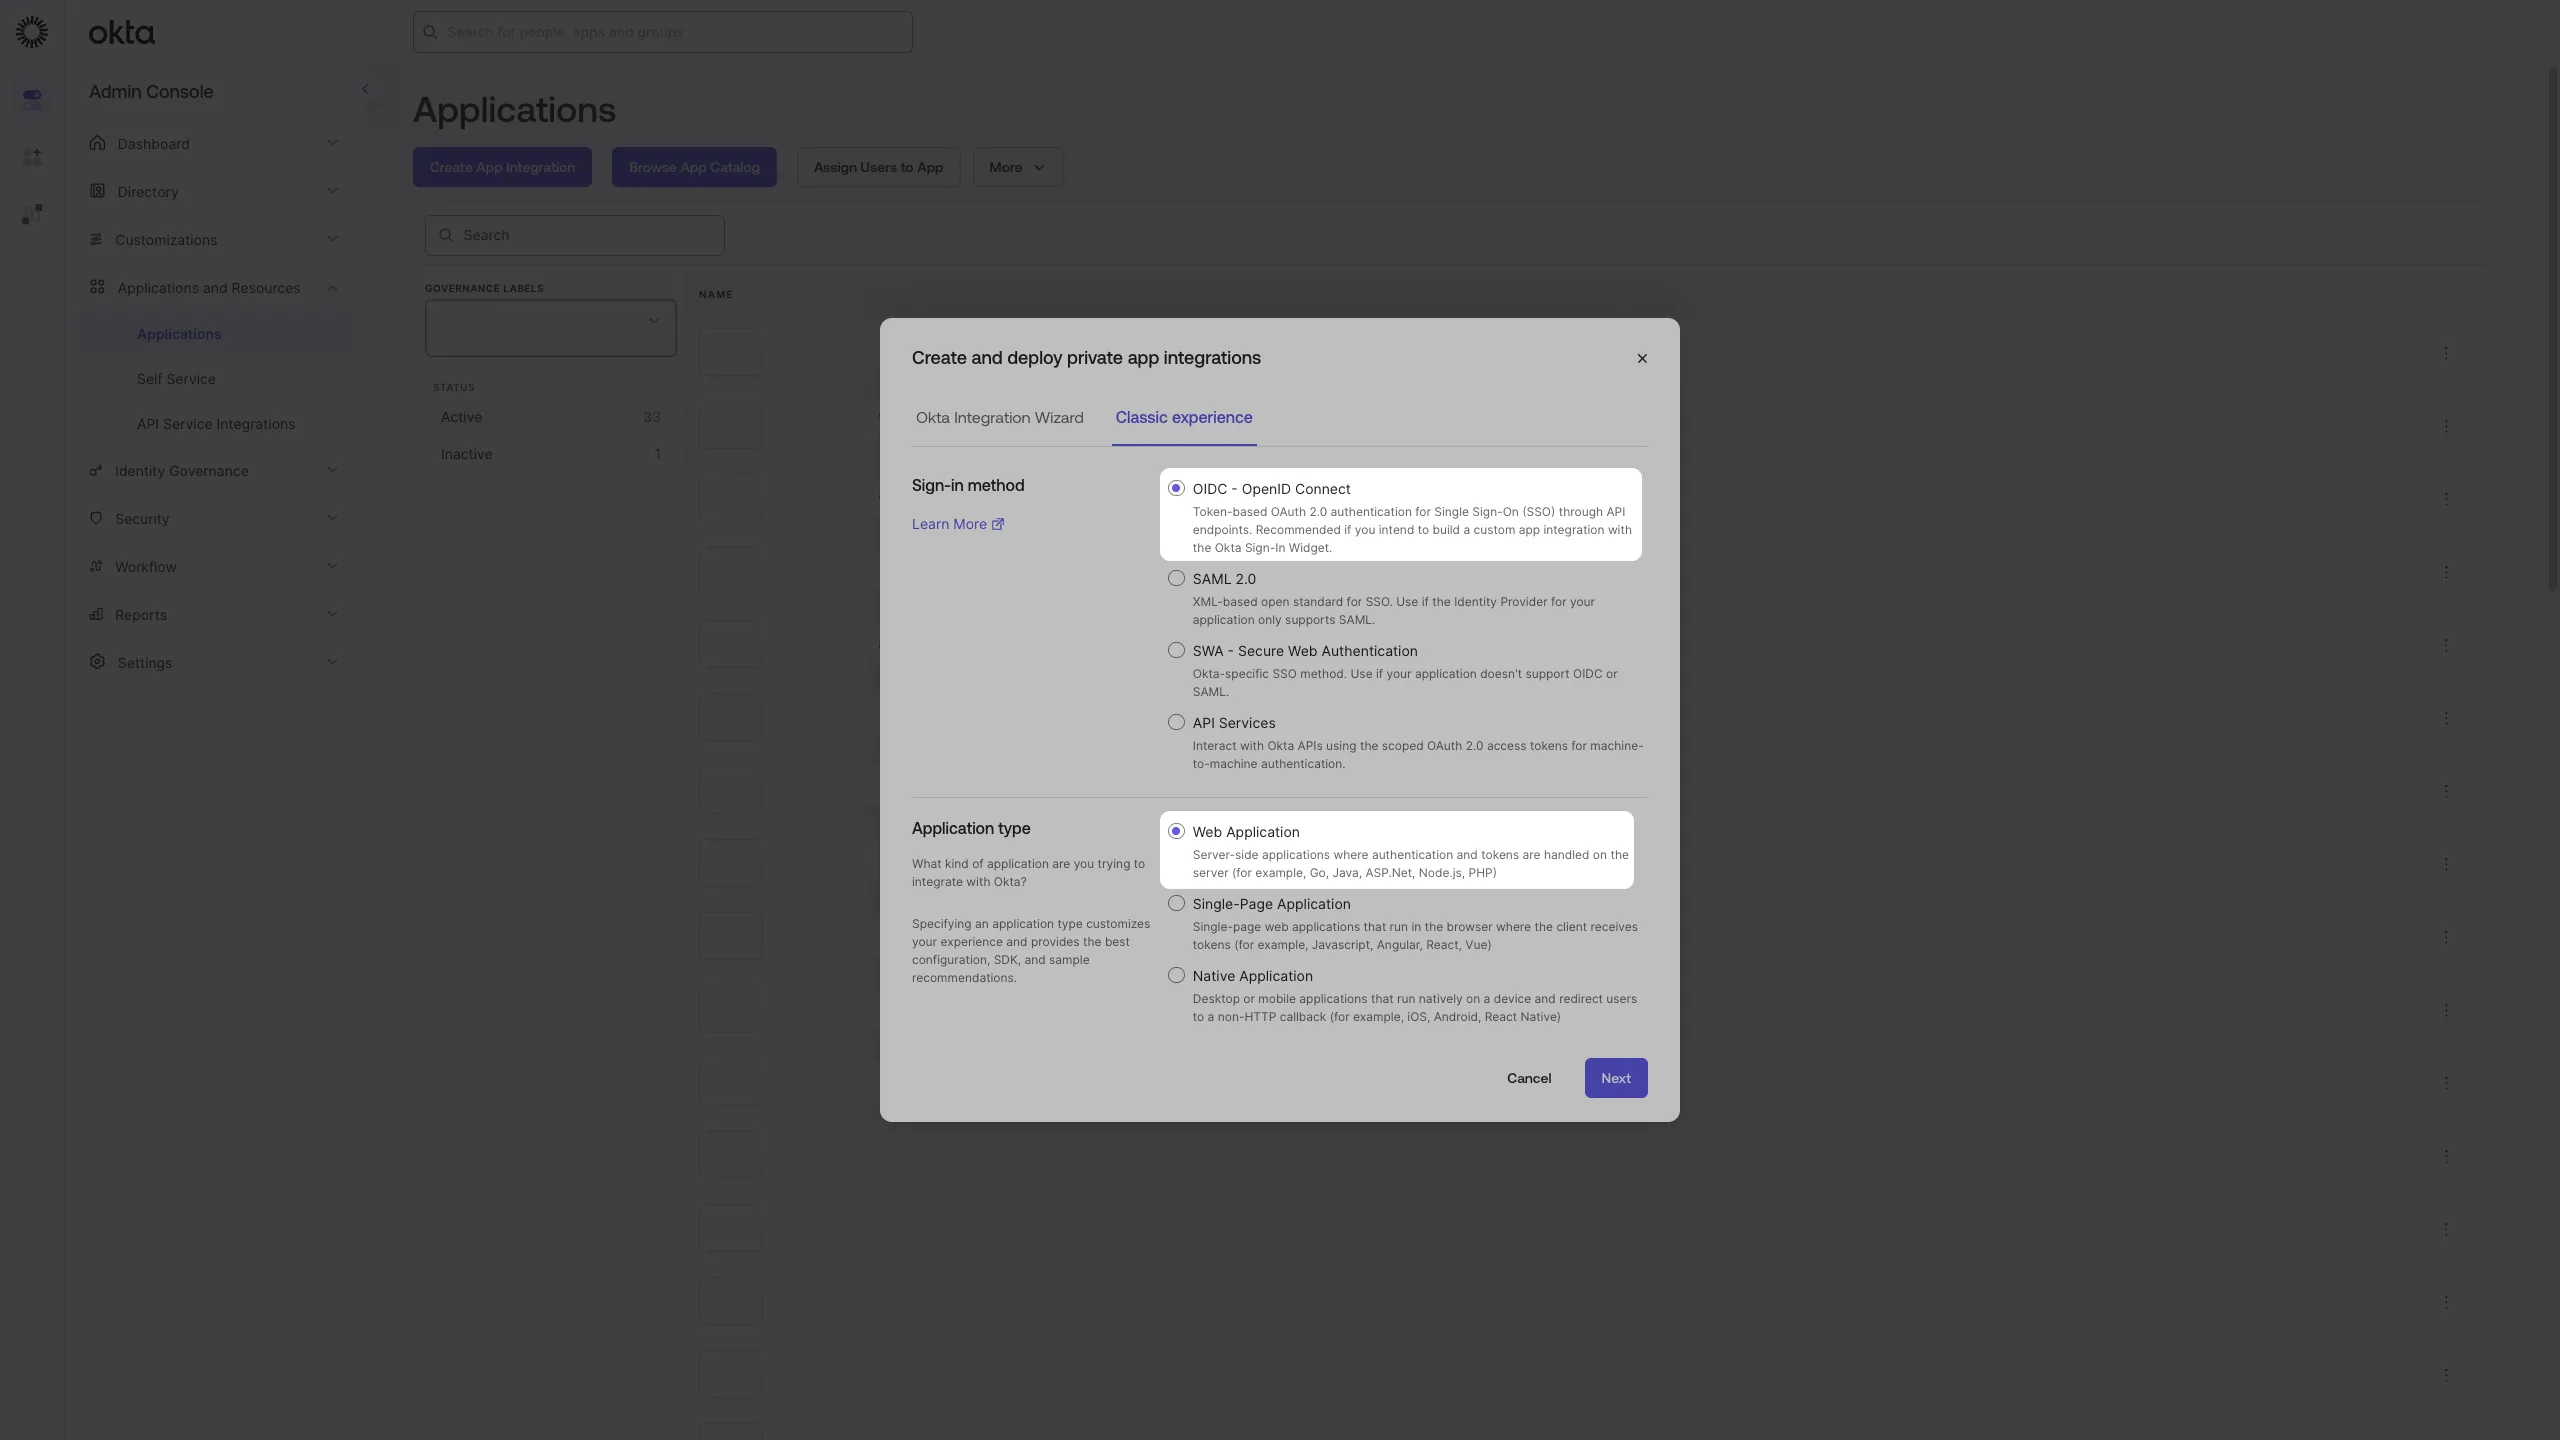
Under Sign-in method, select OIDC - OpenID Connect.
Under Application type, select Web Application.
Select Next.
Step 2: Configure the integration
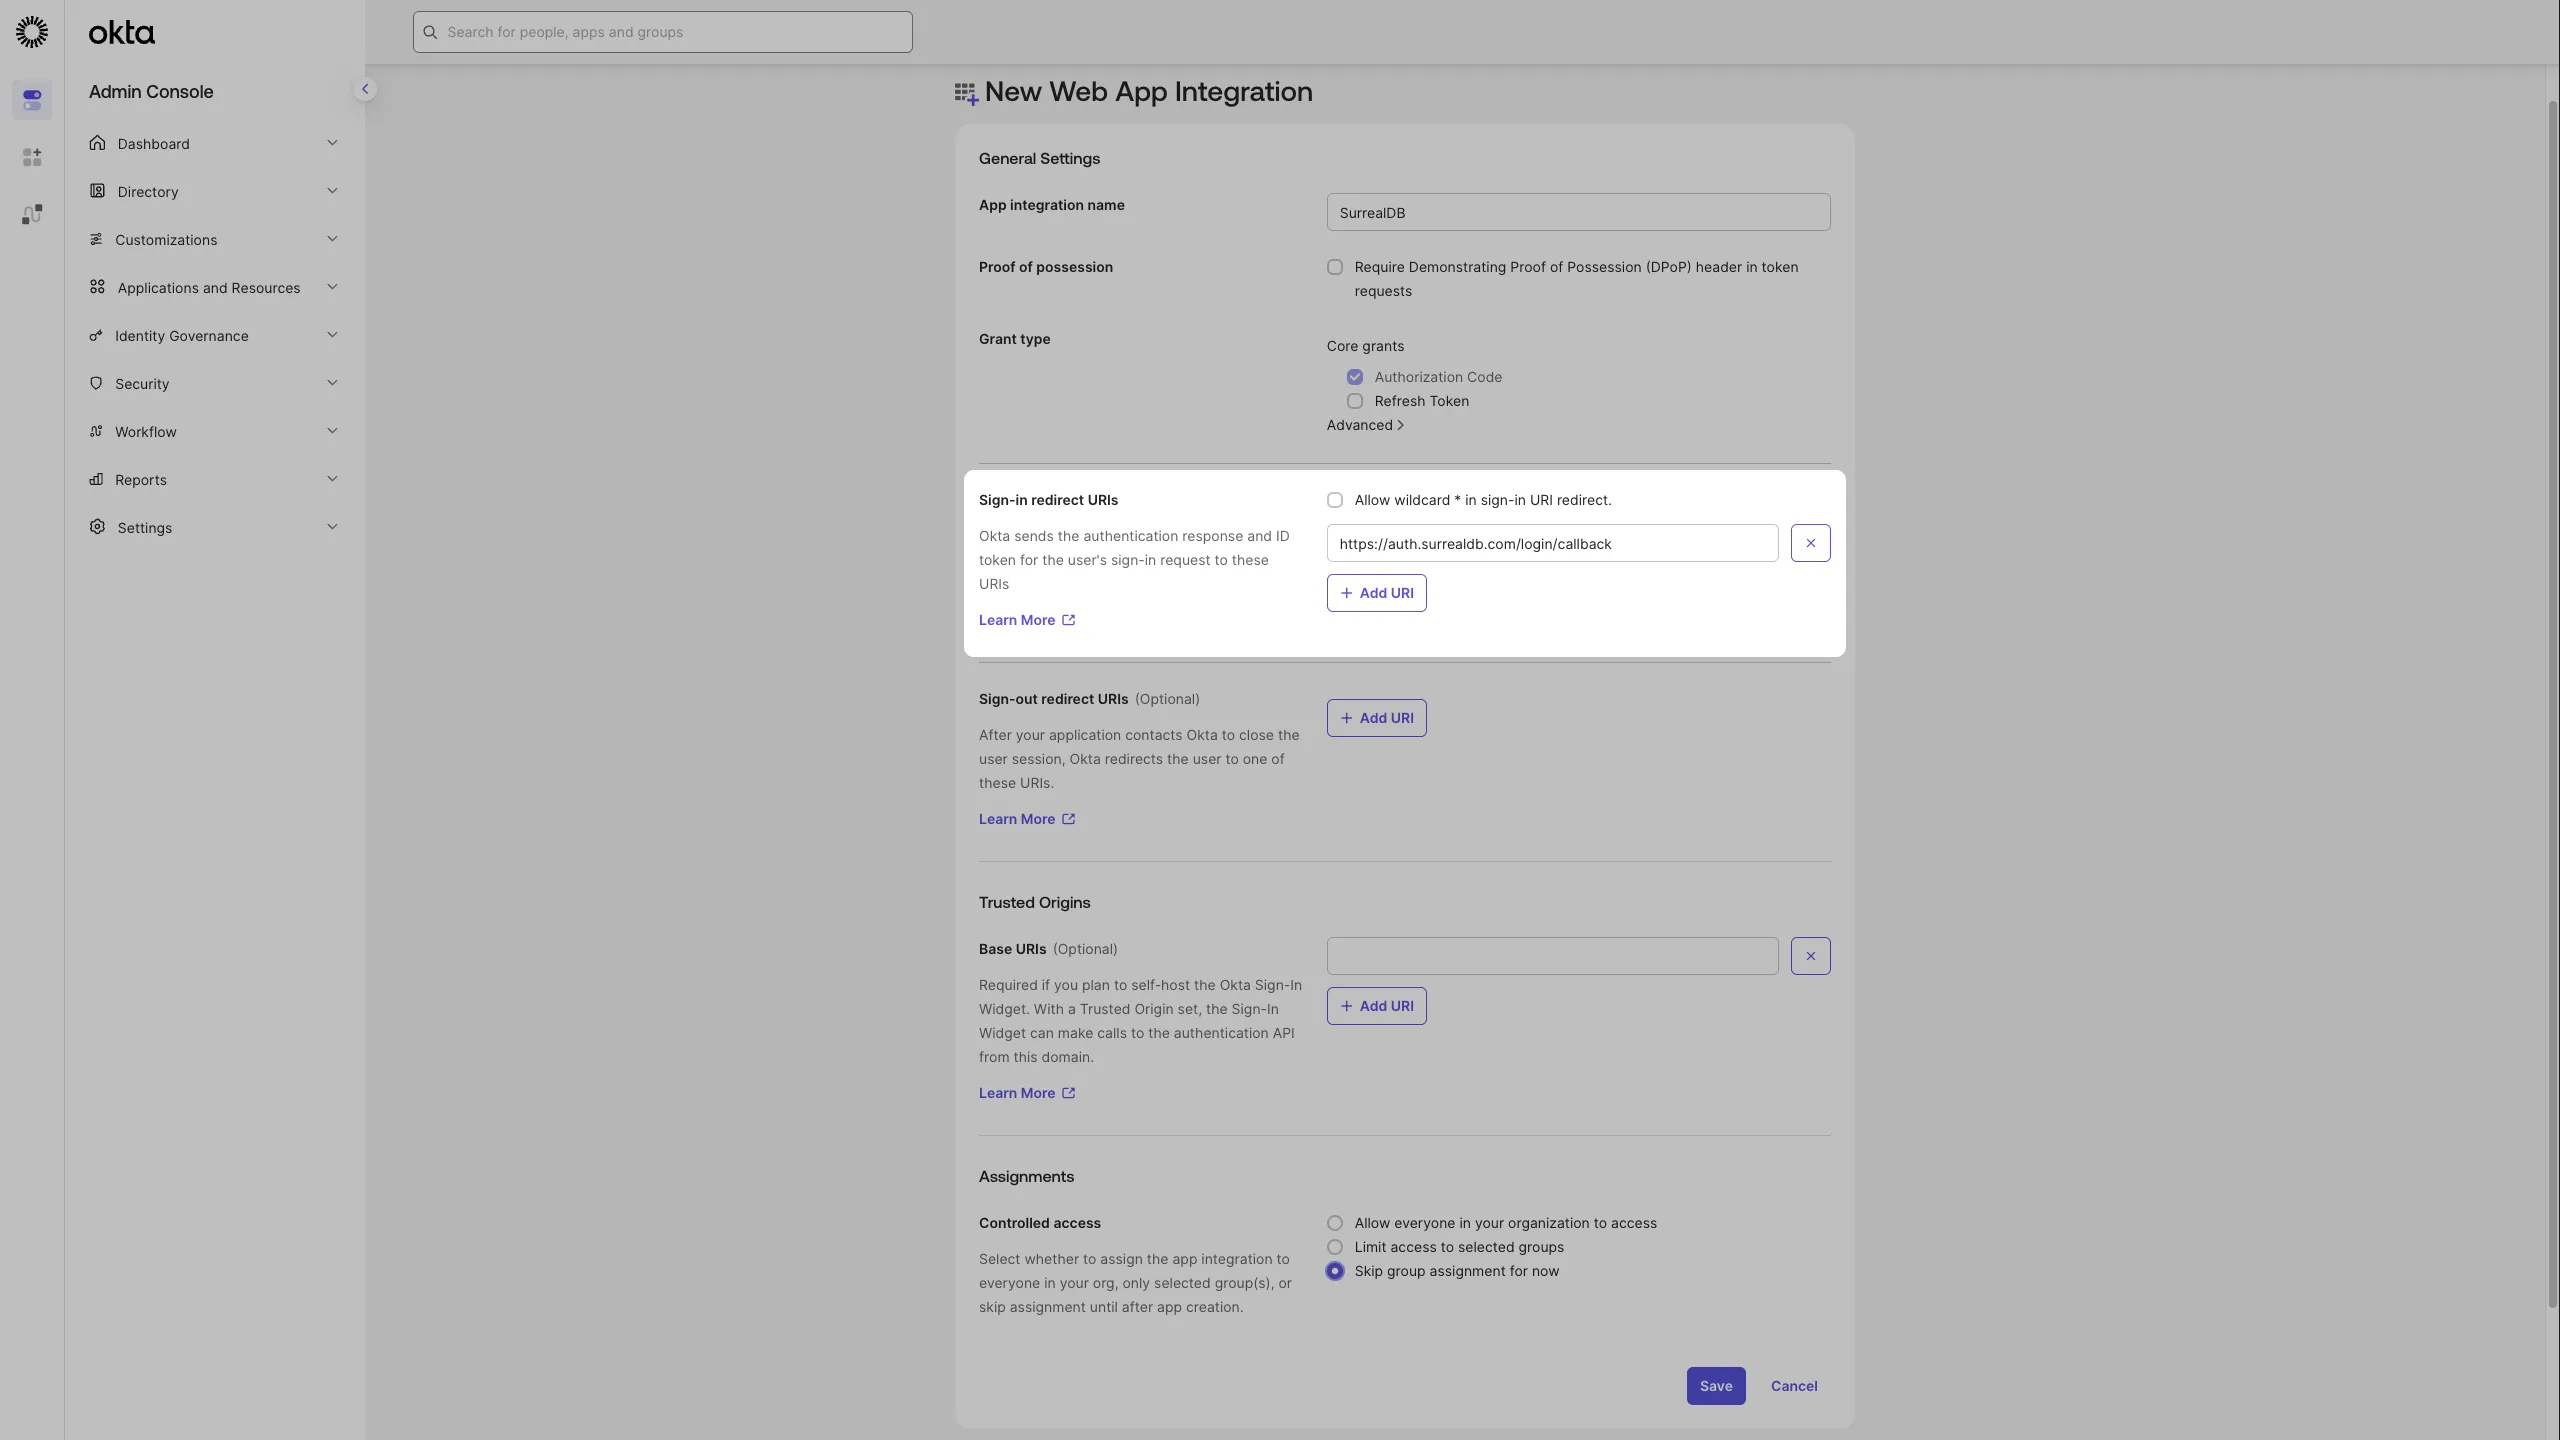
Enter an App integration name, for example
SurrealDB.Under Grant type, make sure Authorization Code is selected.
Under Sign-in redirect URIs, enter
https://auth.surrealdb.com/login/callback.Under Assignments, choose who can use the integration. You can also assign people or groups later, from the integration's Assignments tab.
Select Save.
Only the people and groups assigned to the integration can sign in to SurrealDB through it.
Step 3: Copy the client credentials
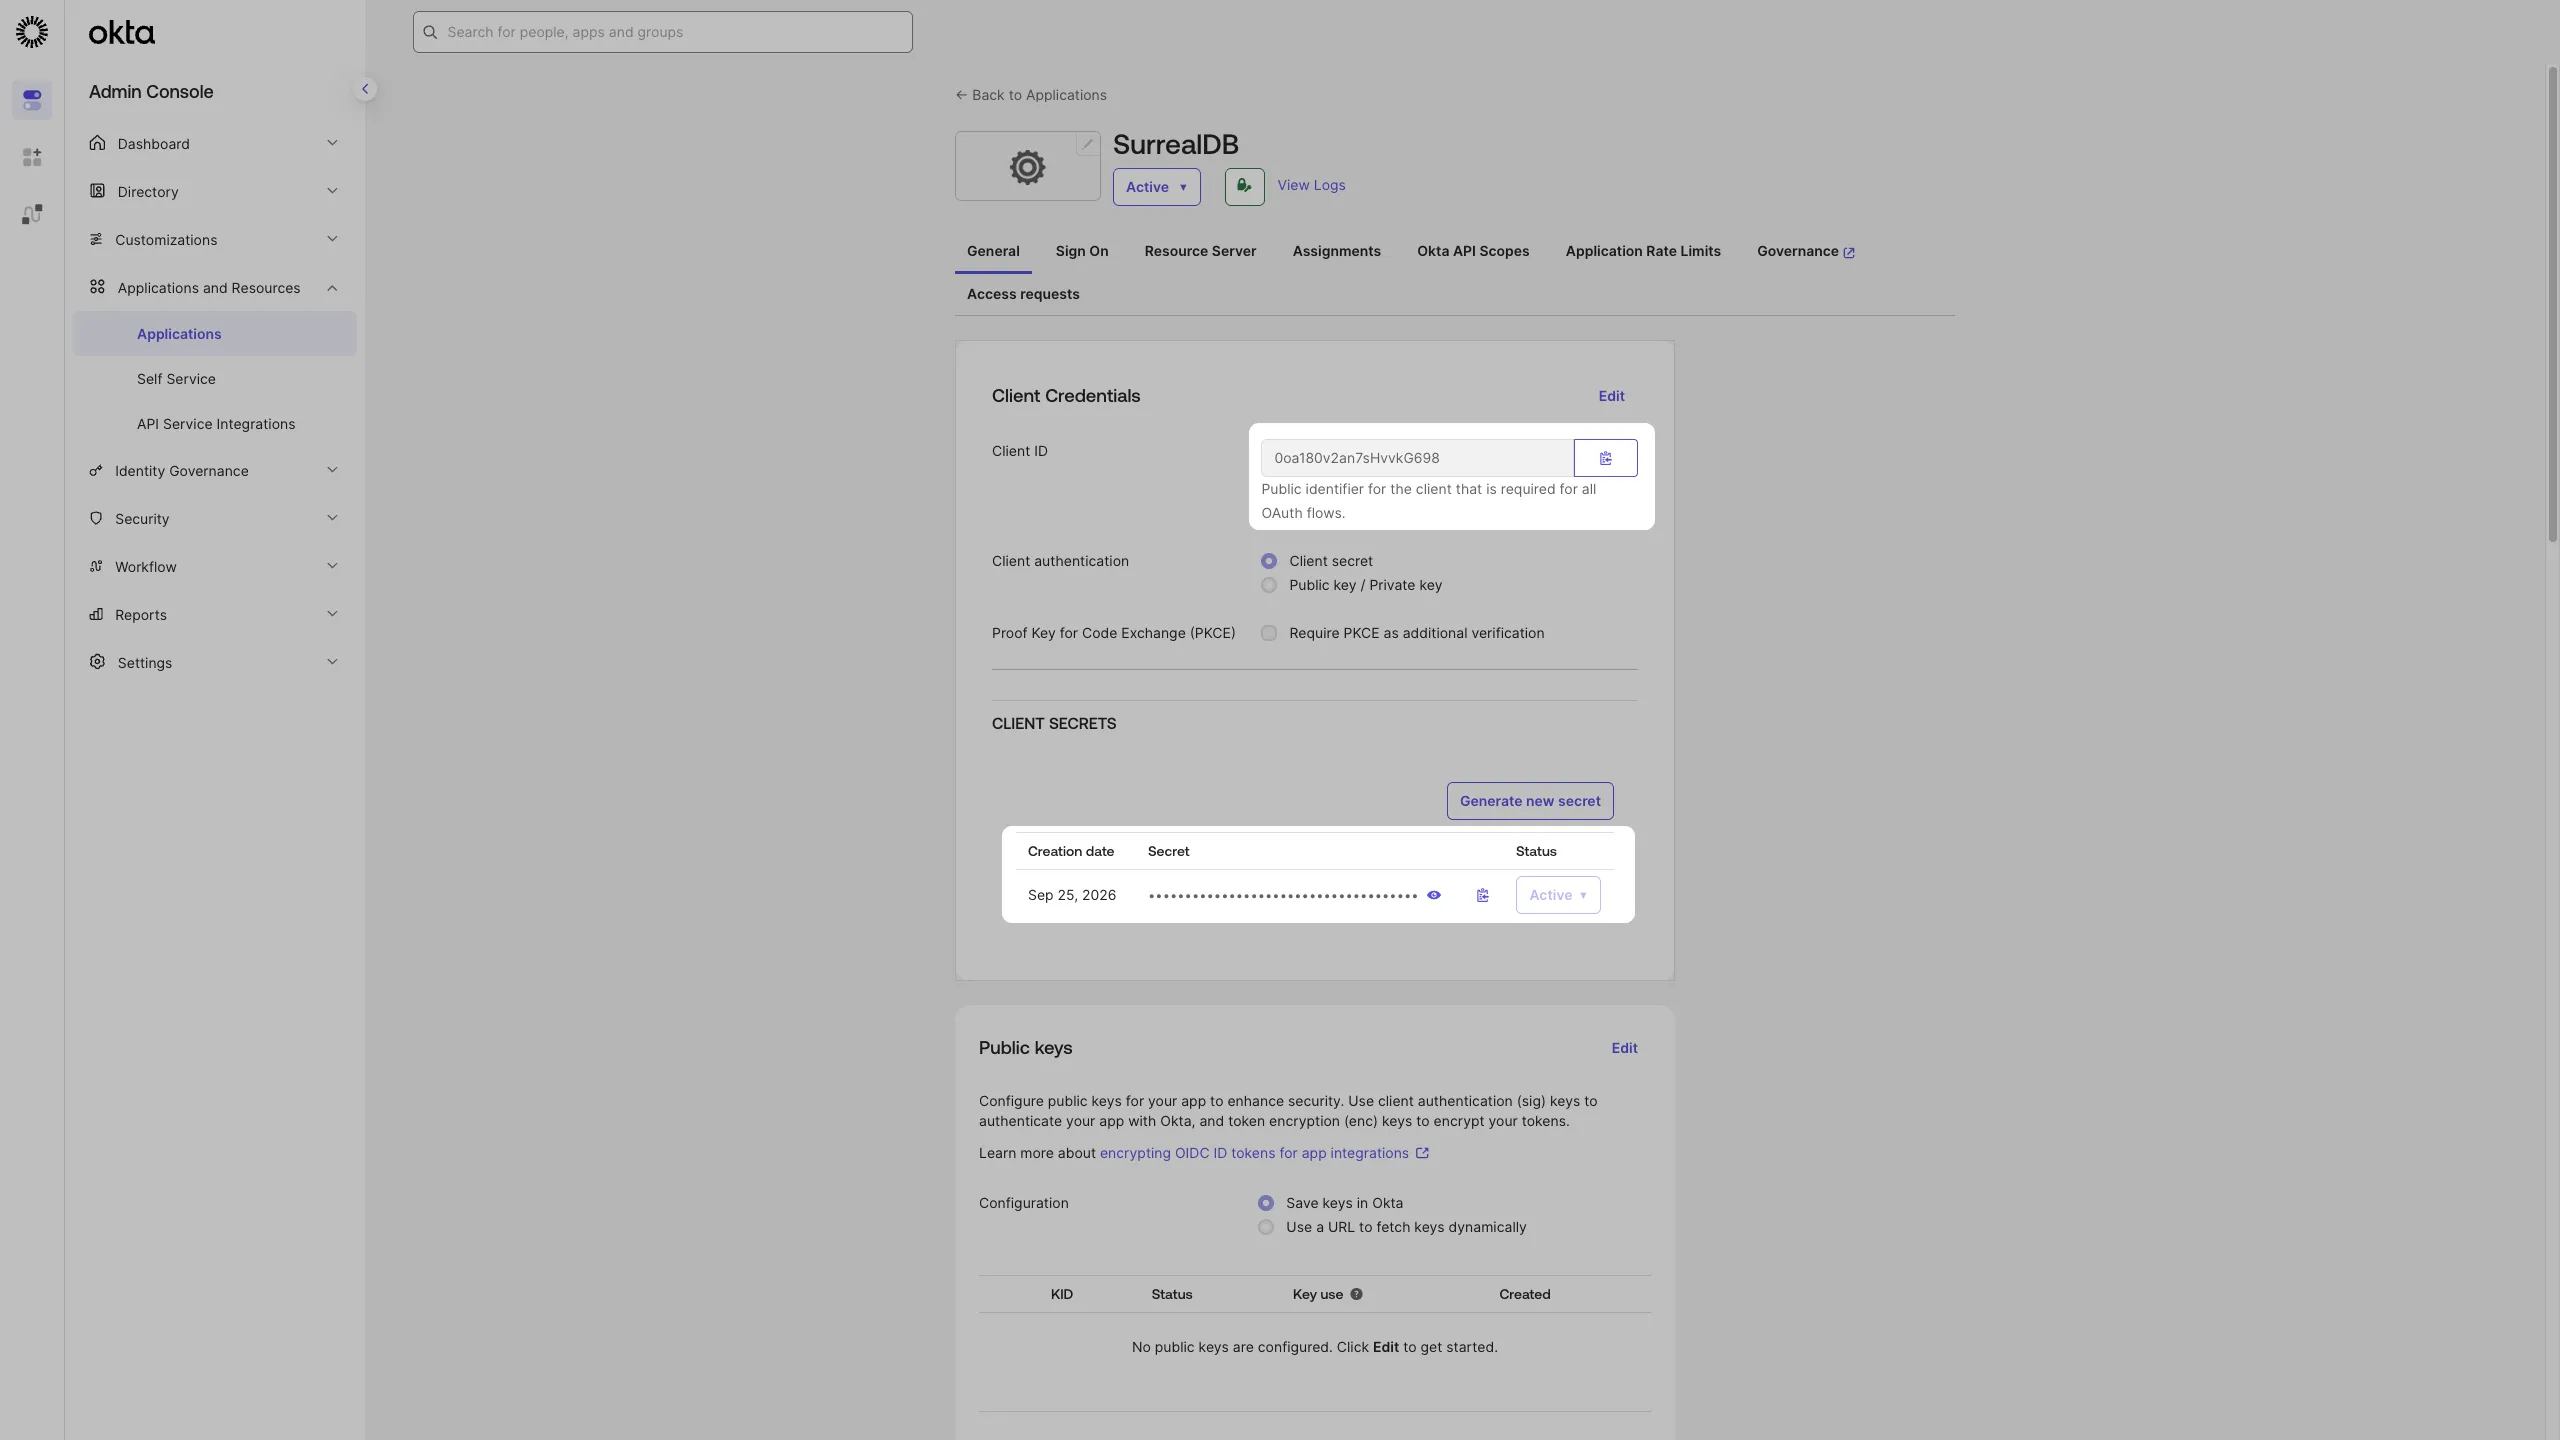
Okta opens the General tab of the new integration.
Under Client Credentials, copy the Client ID.
Under Client secrets, copy the secret. Select the eye icon to show it, or the copy icon beside it.
You also need your Okta domain, for example example.okta.com. It is the domain of your Okta sign-in page, without -admin.
Step 4: Add the connection in SurrealDB
Open Single sign-on in your enterprise and add a new connection.
Select Okta.
Under Name the connection, enter a Display name. Members see this name on the sign-in screen.
Under Enter the Okta details, enter:
Okta domain: your Okta domain, for example
example.okta.com.Client ID: the client ID from step 3.
Scopes: optional. Leave it empty to request
openid profile email.Client secret: the client secret from step 3.
Under Route sign-in domains, select the verified domains to send to this connection. This is optional, and you can change it later.
Select Create connection.
The Set up Okta section of the form shows the redirect URI, with a copy button beside it, if you need it again.
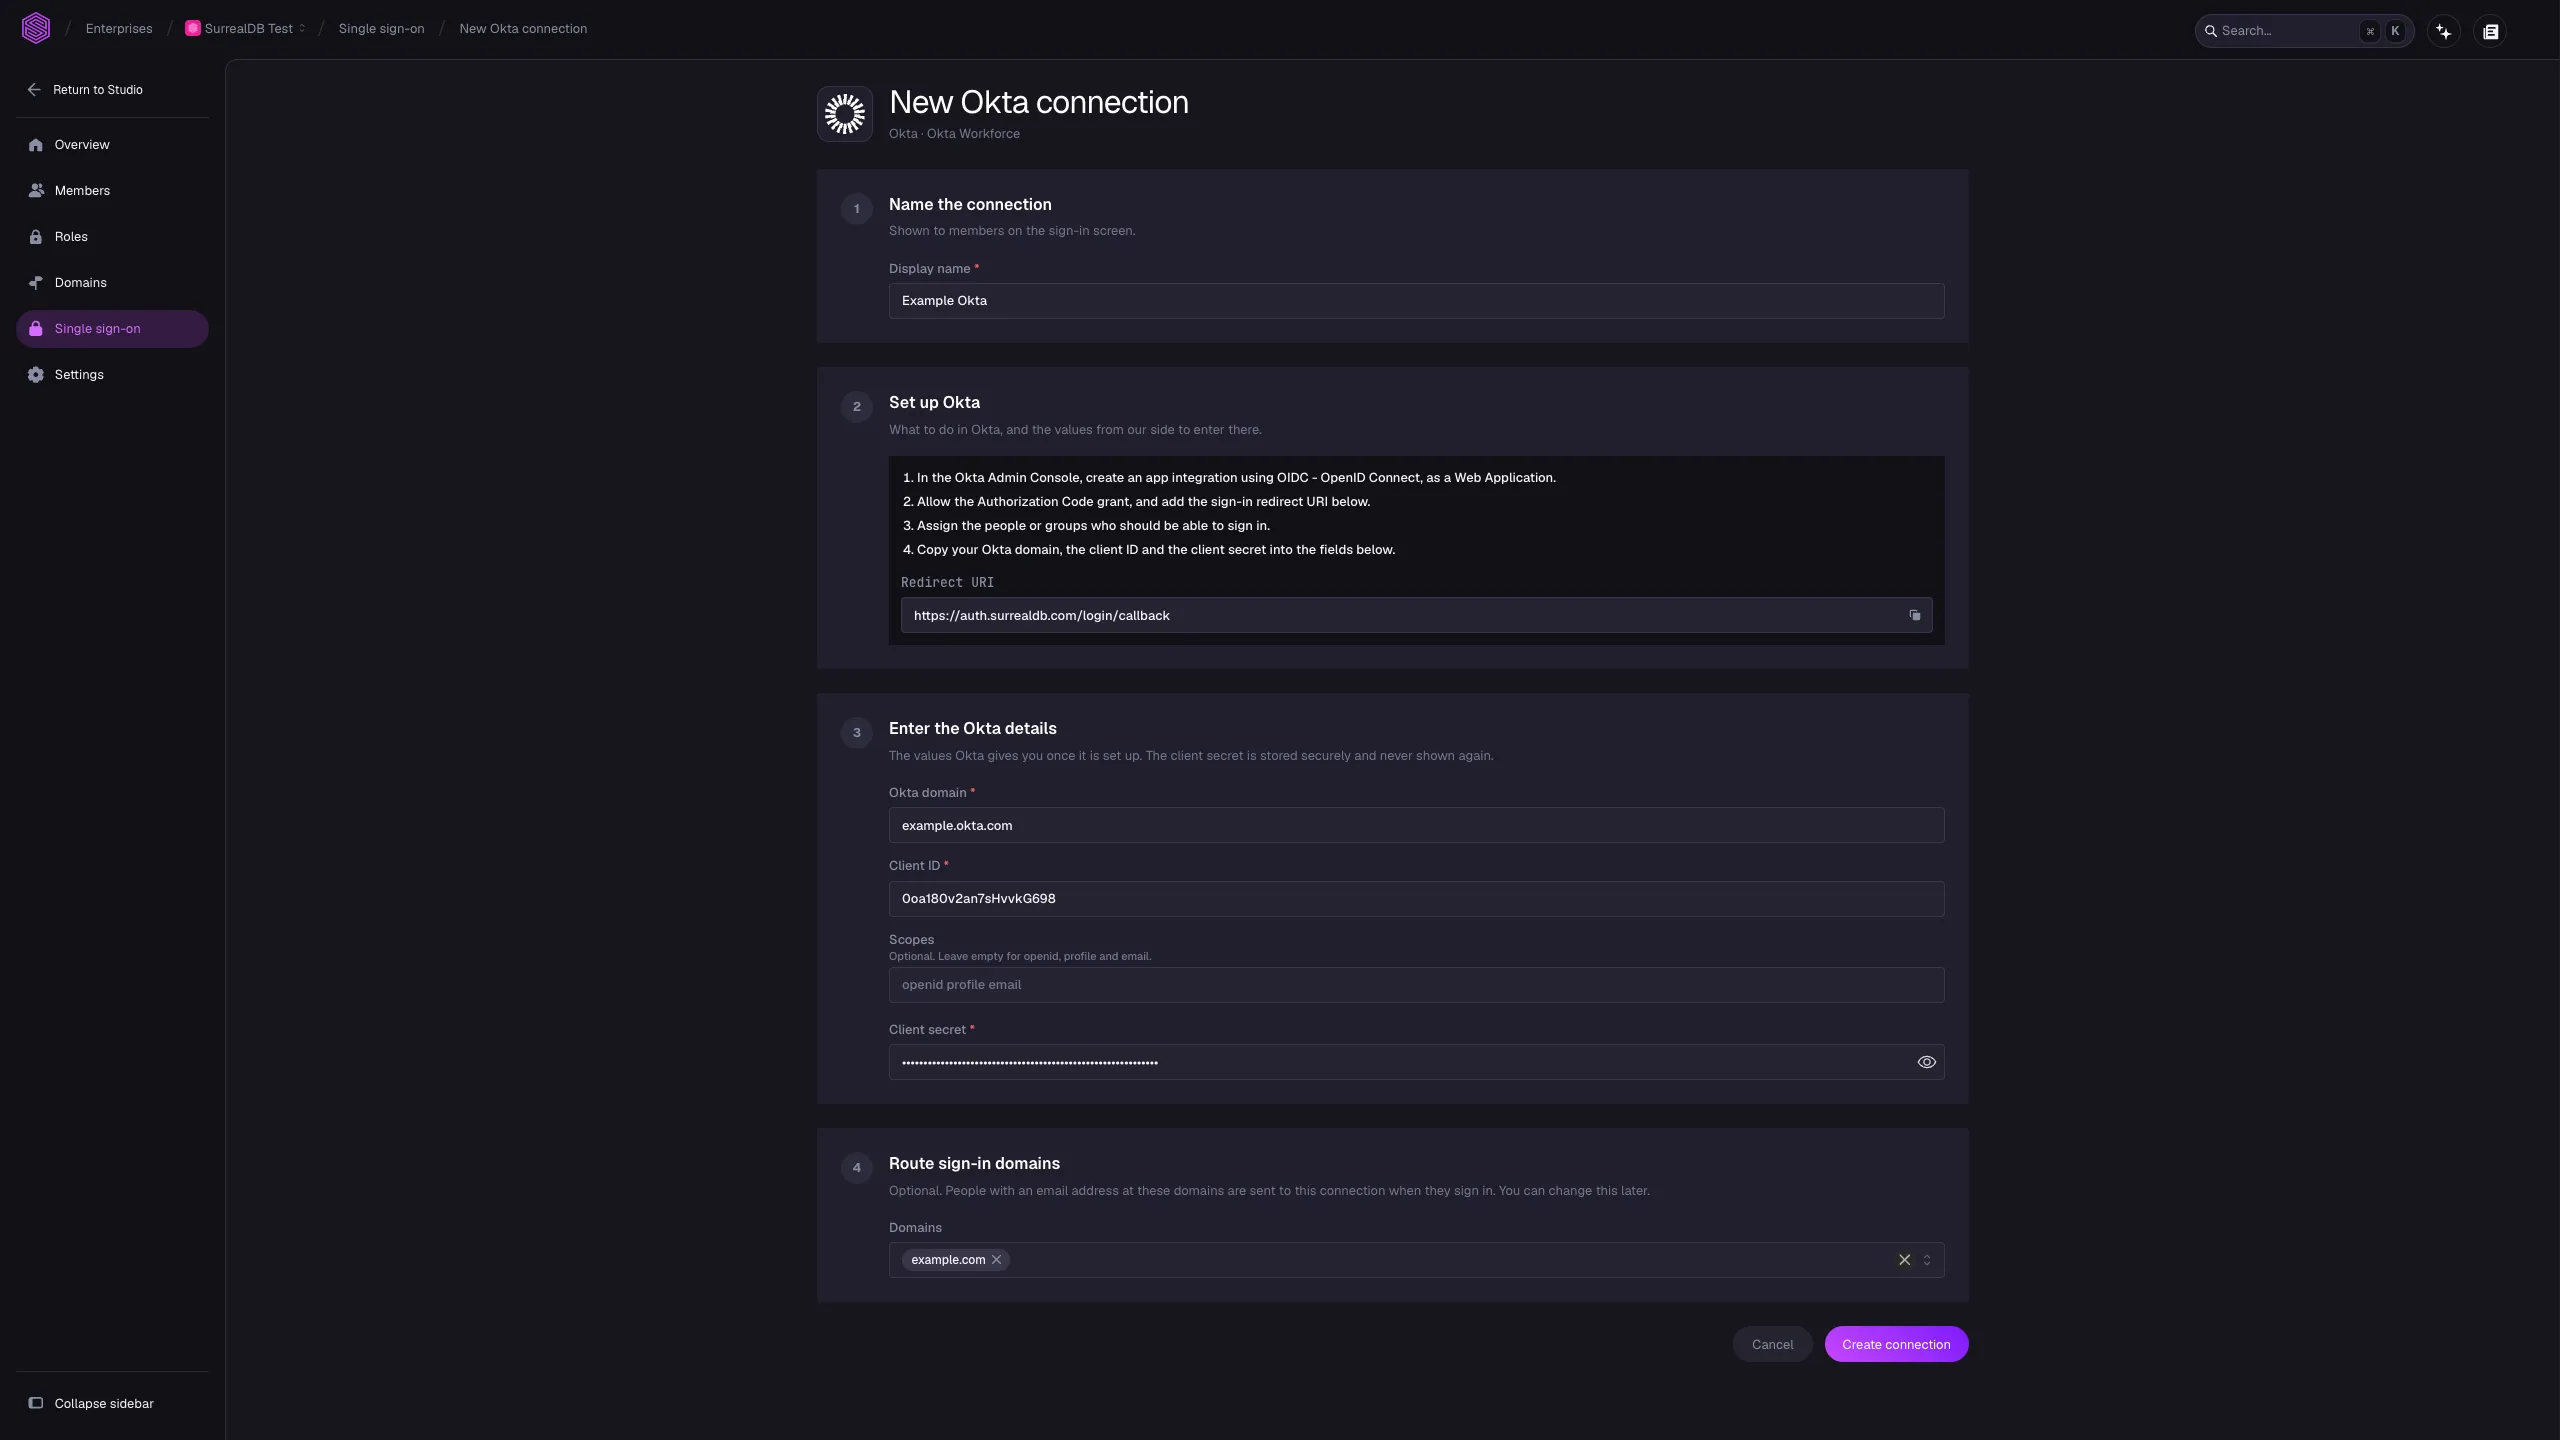
SurrealDB stores the client secret securely and does not show it again.
Next steps
If you did not route a domain when you created the connection, route one now. Then choose the applications that people can sign in to with this connection.